A supertanker went dark for thirty hours in the middle of the ocean, and almost nobody is asking the question that actually matters. Not whether it was hacked. Whether the entire surveillance system the energy trading world relies on just quietly stopped working.
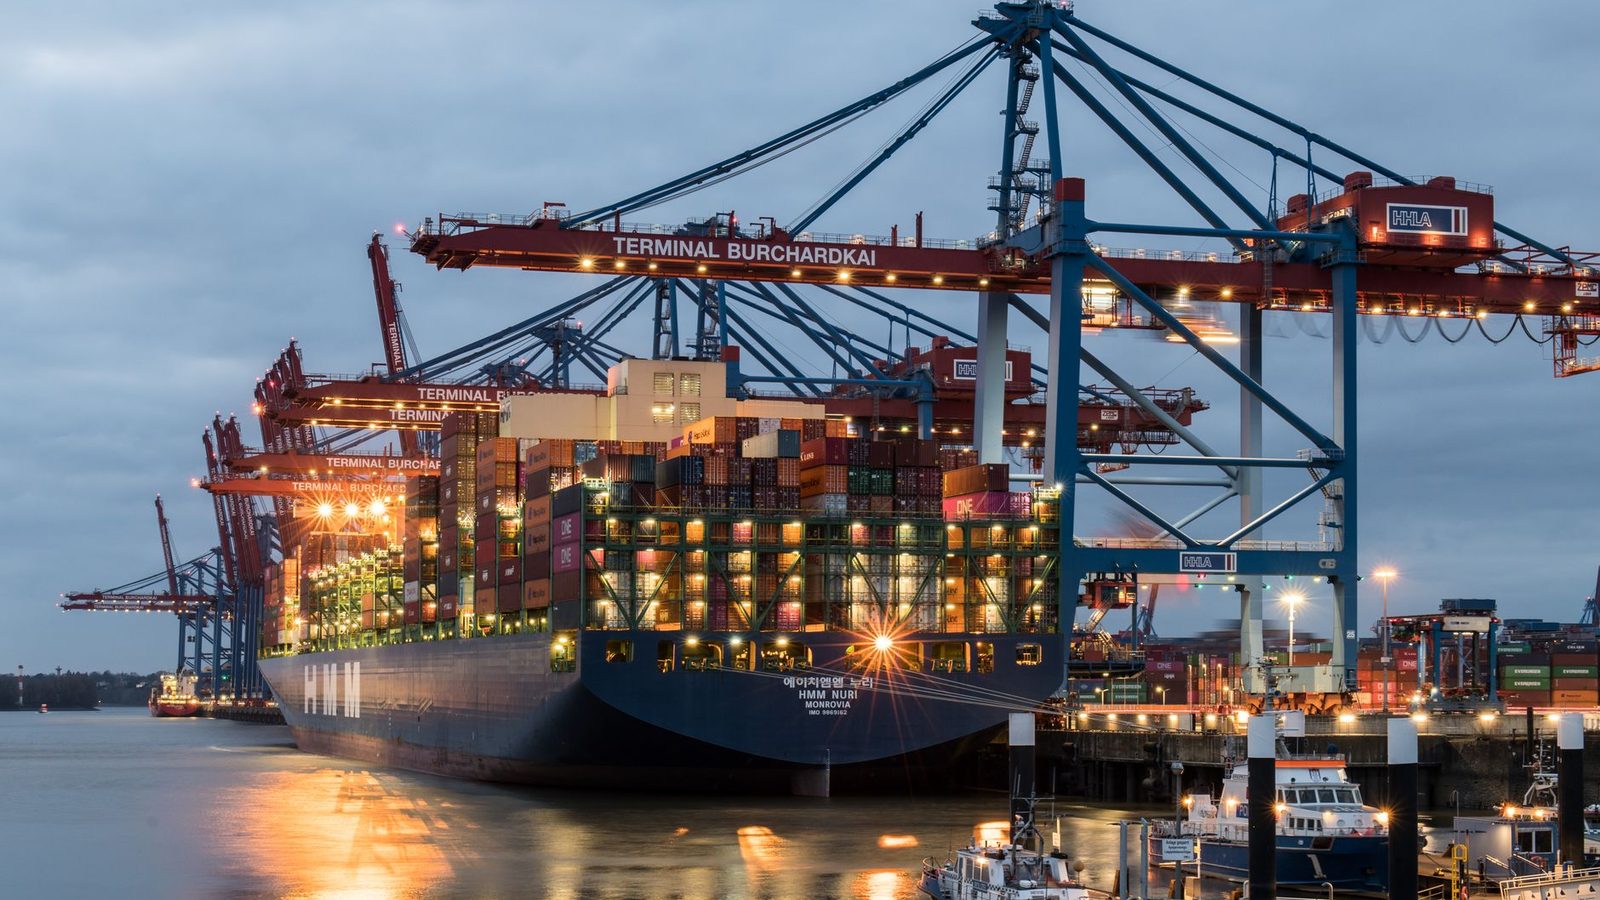
In early August, the VL Prosperity, a Liberian-flagged very large crude carrier managed by South Korea's HMM Ocean Service, was sailing from Egypt's Sidi Kerir terminal toward the United States when it reportedly lost communications for around thirty hours. By late August, the US Coast Guard and FBI had boarded the vessel off the Texas coast to run a full cyber security investigation. A separate LNG carrier was also inspected over a suspected compromise. Authorities are now said to be tracking cyber threats against close to twenty ships worldwide. This is not a one-off curiosity. It is a pattern, and patterns are what move markets.
The mechanism everyone is getting wrong
The instinctive read is ransomware, or a nation-state prank on navigation systems, filed under generic cybersecurity risk. That framing misses the mechanism entirely. The transmission channel here is not IT security budgets. It is trust in vessel tracking data itself, and that data is the backbone of an entire compliance and pricing architecture built to enforce sanctions on Russian and Iranian oil.
Shadow fleet vessels evade sanctions by disabling AIS transponders, spoofing GPS position, and going dark for stretches of a voyage. Banks, insurers, and refiners have built their entire counterparty risk framework around exactly this signature: a communications or tracking gap means suspect cargo, clean continuous tracking means a compliant vessel. That is the whole verification model. It is cheap, it is automated, and every major trading desk and marine insurer leans on it.
A compliant, properly flagged, professionally managed supertanker just produced the identical signature, thirty hours of silence, mid-voyage, for reasons that appear to be malicious interference rather than sanctions evasion. The market has this exactly backwards if it treats this as a shipping security story. It is a data integrity story. The signal that the entire sanctions enforcement industry depends on can now be manufactured or disrupted by a third party with no connection to the vessel's actual cargo or intent.
The second-order effect nobody is pricing
Once a communications blackout can be forced onto a vessel that is doing nothing wrong, the binary heuristic collapses. Insurers cannot cleanly separate shadow fleet behavior from hacked-vessel behavior using tracking data alone. Compliance teams at trading houses and banks now have to treat every unexplained AIS gap as ambiguous rather than diagnostic. That does not show up as a headline. It shows up slowly, as higher due diligence costs, longer clearance times on cargo documentation, and wider marine war risk premiums that get quietly absorbed into freight rates rather than announced anywhere.
This is the underpriced risk. Not that a tanker gets hacked. That the verification infrastructure underpinning sanctions enforcement on seaborne energy trade just lost a meaningful chunk of its reliability, at the exact moment shadow fleet volumes are already at multi-year highs and enforcement pressure is intensifying rather than easing.
The honest counter-case
This could still be nothing more than an isolated intrusion, opportunistic and unrelated to sanctions dynamics at all. Maritime cyber incidents have been rising for years across ransomware and GPS interference without producing any systemic repricing of shipping or insurance. If investigators confirm a narrow, contained cause with no broader targeting pattern, the twenty-vessel tracking figure could simply reflect heightened vigilance rather than an active campaign, and the compliance friction I am describing may never materialize at scale. That is a real possibility, not a hedge sentence.
What would change my view: evidence that the intrusions are opportunistic criminal activity with no state fingerprint, and no measurable widening in marine war risk premiums over the next two quarters. Absent that, the compliance drag compounds quietly.
Running this through a delta-neutral volatility lens, the interesting exposure is not directional on tanker operators or energy names. It is in how marine insurance underwriting and shipping compliance costs get repriced across the book, independent of where crude or LNG prices go. The mechanism is not priced yet, and it will not announce itself when it starts to be.
What I am watching next: whether US or allied authorities confirm a state actor behind any of the roughly twenty vessels under scrutiny, and whether marine war risk premiums start moving before the next sanctions package lands. If your desk still treats an AIS gap as a clean signal, ask yourself what you are actually measuring now.
Common questions
What happened with the VL Prosperity tanker cyberattack?
The VL Prosperity, a Liberian-flagged very large crude carrier managed by HMM Ocean Service, reportedly lost communications for roughly 30 hours in early August while sailing from Egypt toward the United States. The US Coast Guard and FBI boarded the vessel off the Texas coast in late August to investigate whether its onboard network had been compromised by hackers.
Was more than one ship affected?
A second vessel, an LNG carrier, was also inspected by US authorities over a suspected cyberattack. Reporting has indicated the US is monitoring cyber threats against close to twenty ships worldwide, suggesting the VL Prosperity case is part of a broader pattern rather than an isolated incident.
Is this related to sanctions on Russian or Iranian oil?
There is no confirmed link stated by US authorities, but the incident occurred against a backdrop of expanding shadow fleet sanctions activity, where vessels routinely disable location tracking to obscure the origin and destination of sanctioned cargo. The overlap in method between shadow fleet evasion tactics and this reported hack is notable, not confirmed as coordinated.
How does a tanker cyberattack affect energy markets?
The direct operational disruption from a single vessel losing communications is minor. The more relevant transmission channel is through marine insurance underwriting, sanctions compliance costs for charterers and banks, and the reliability of vessel tracking data that energy trading desks and insurers depend on to assess counterparty risk.
Does this change how investors should think about shipping and energy stocks?
This is general commentary, not investment advice. What it does change is the confidence level placed on AIS and vessel tracking data as a clean signal for compliance and risk pricing across tanker operators, marine insurers, and commodity trading desks that rely on that data.